ไข่ส้มวิทยา ไข่ส้มวิทยา
Module 3: Transactions & Digital Keys • Episode 19

Public Keys: Elliptic Curve Multiplication (secp256k1)

Elliptic curve mathematics (secp256k1) and compressed public key representations.

#BitcoinBeginner #PublicKey #EllipticCurve #secp256k1
Cover slide for Episode 19: Public Keys: Elliptic Curve Multiplication (secp256k1)
🔍 Tap to expand
Slides for Episode 19 — Tap to view full screen

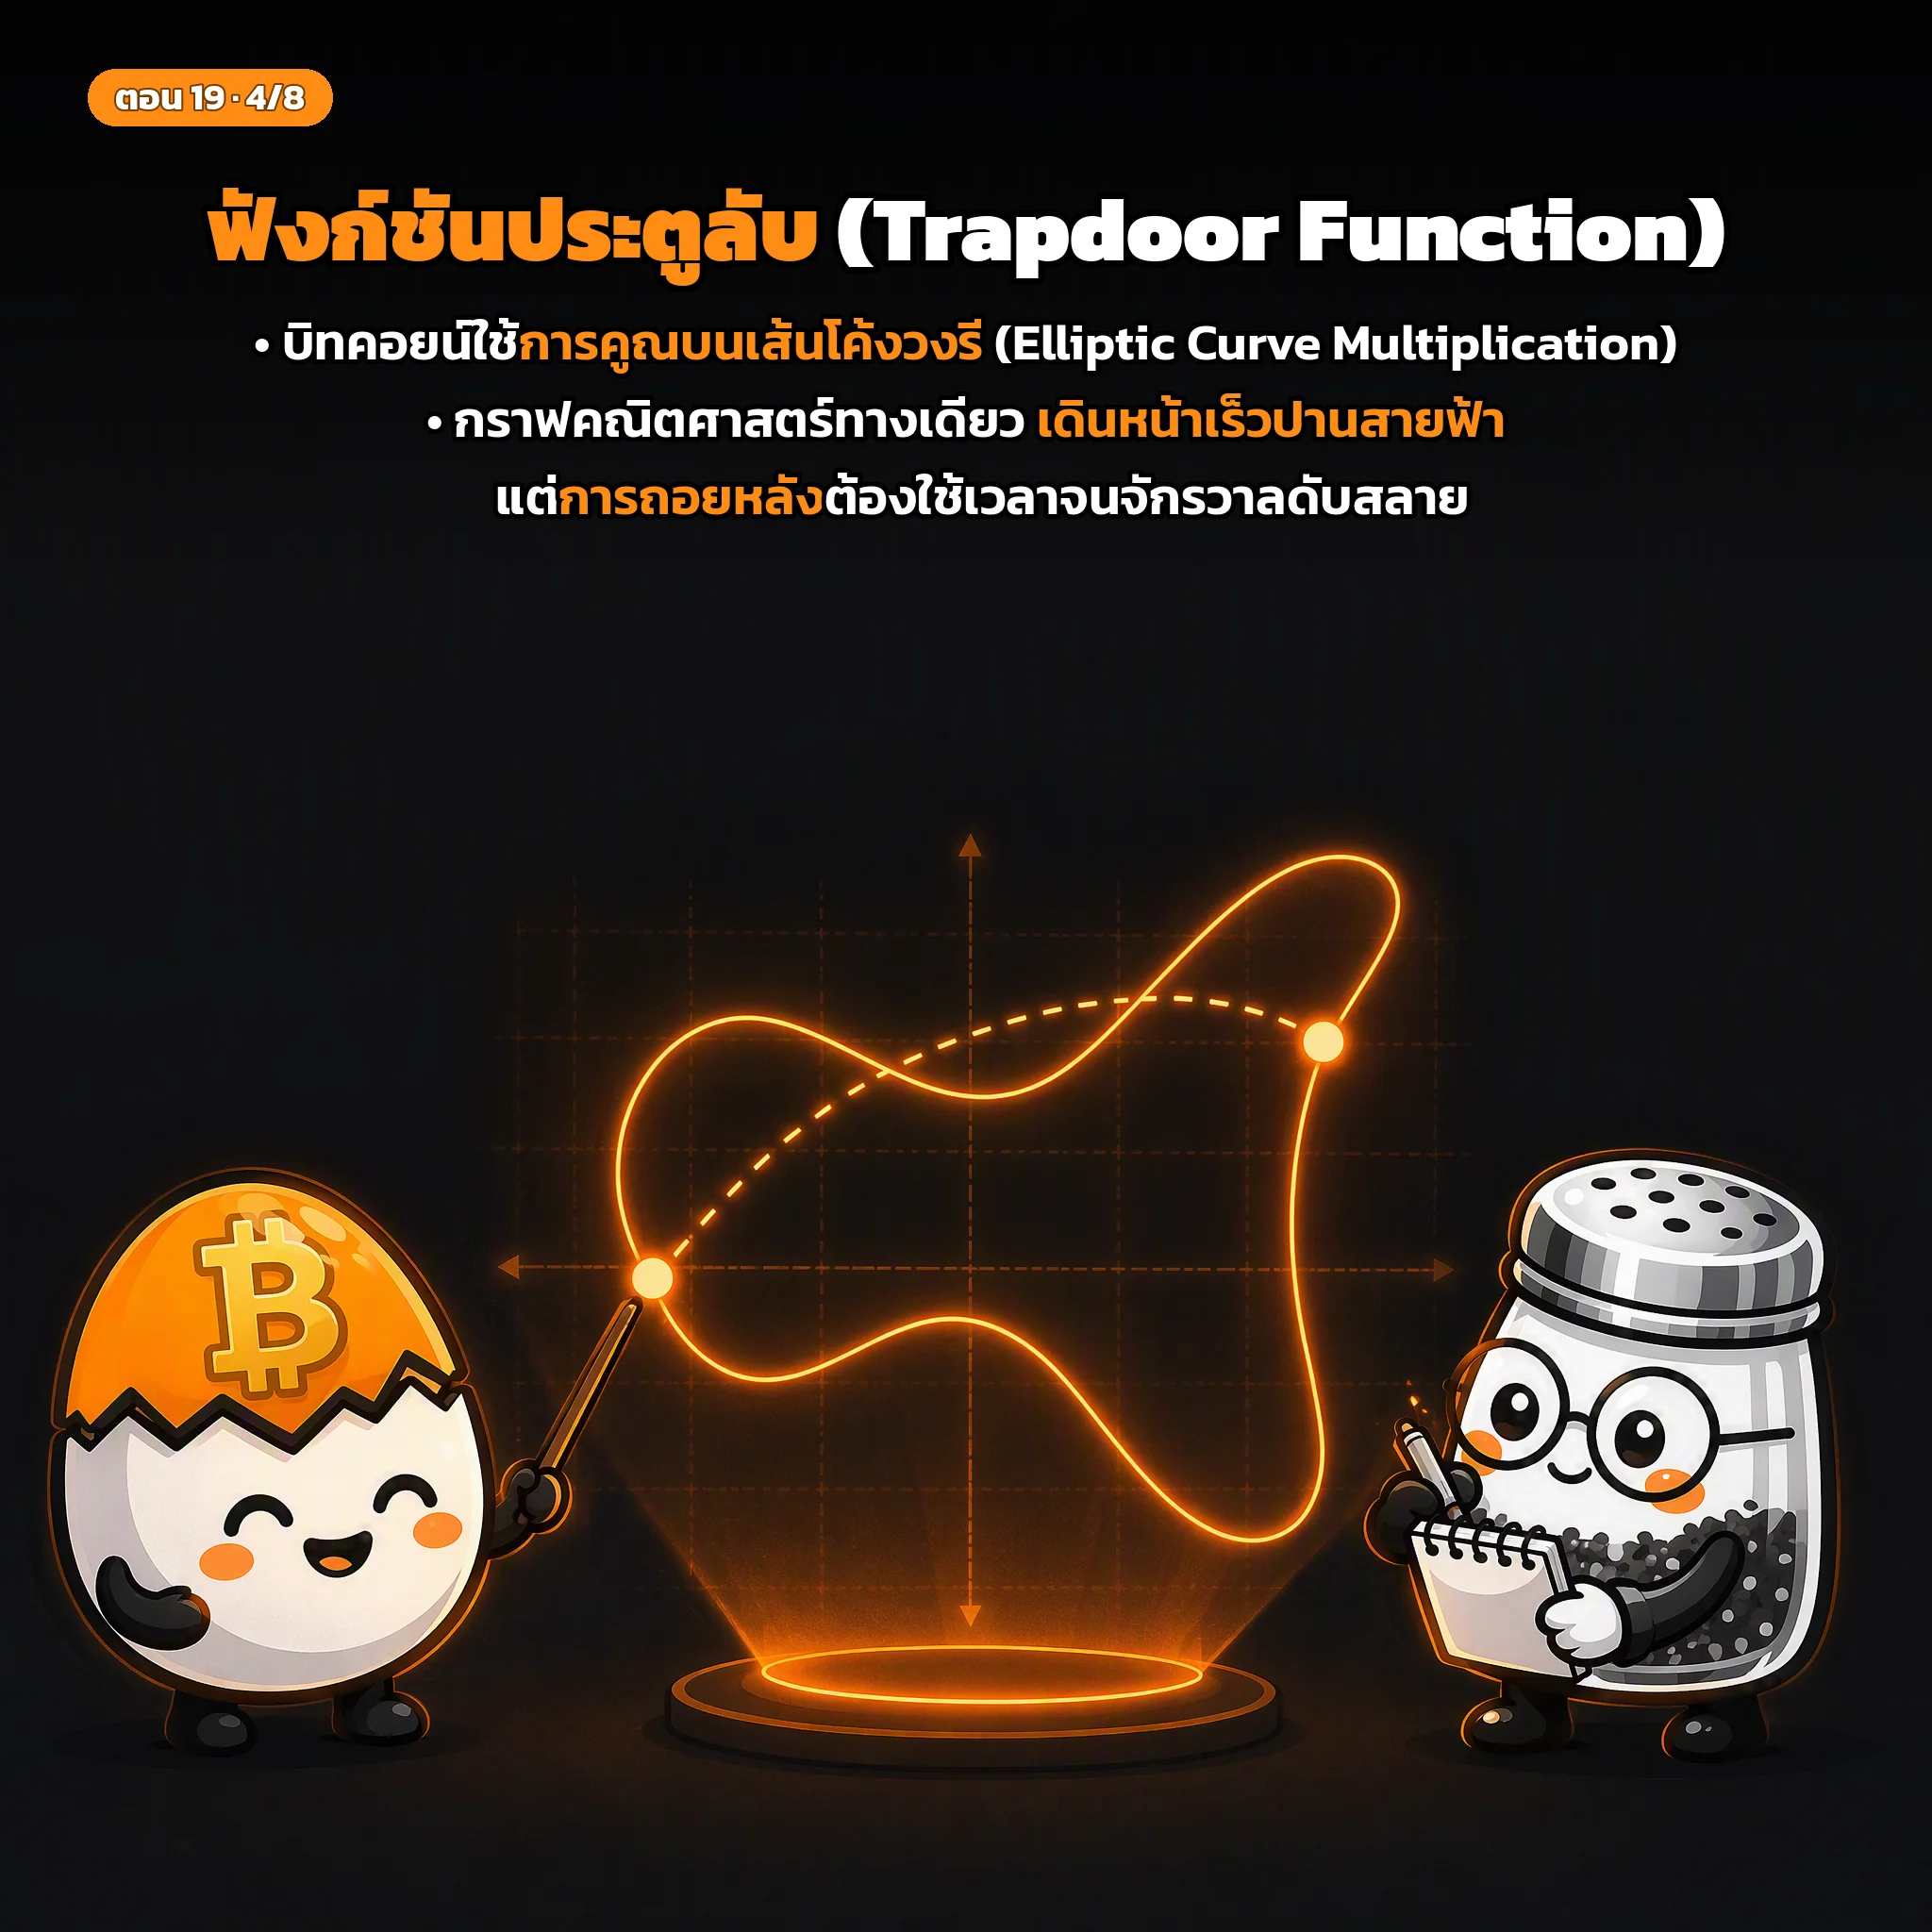
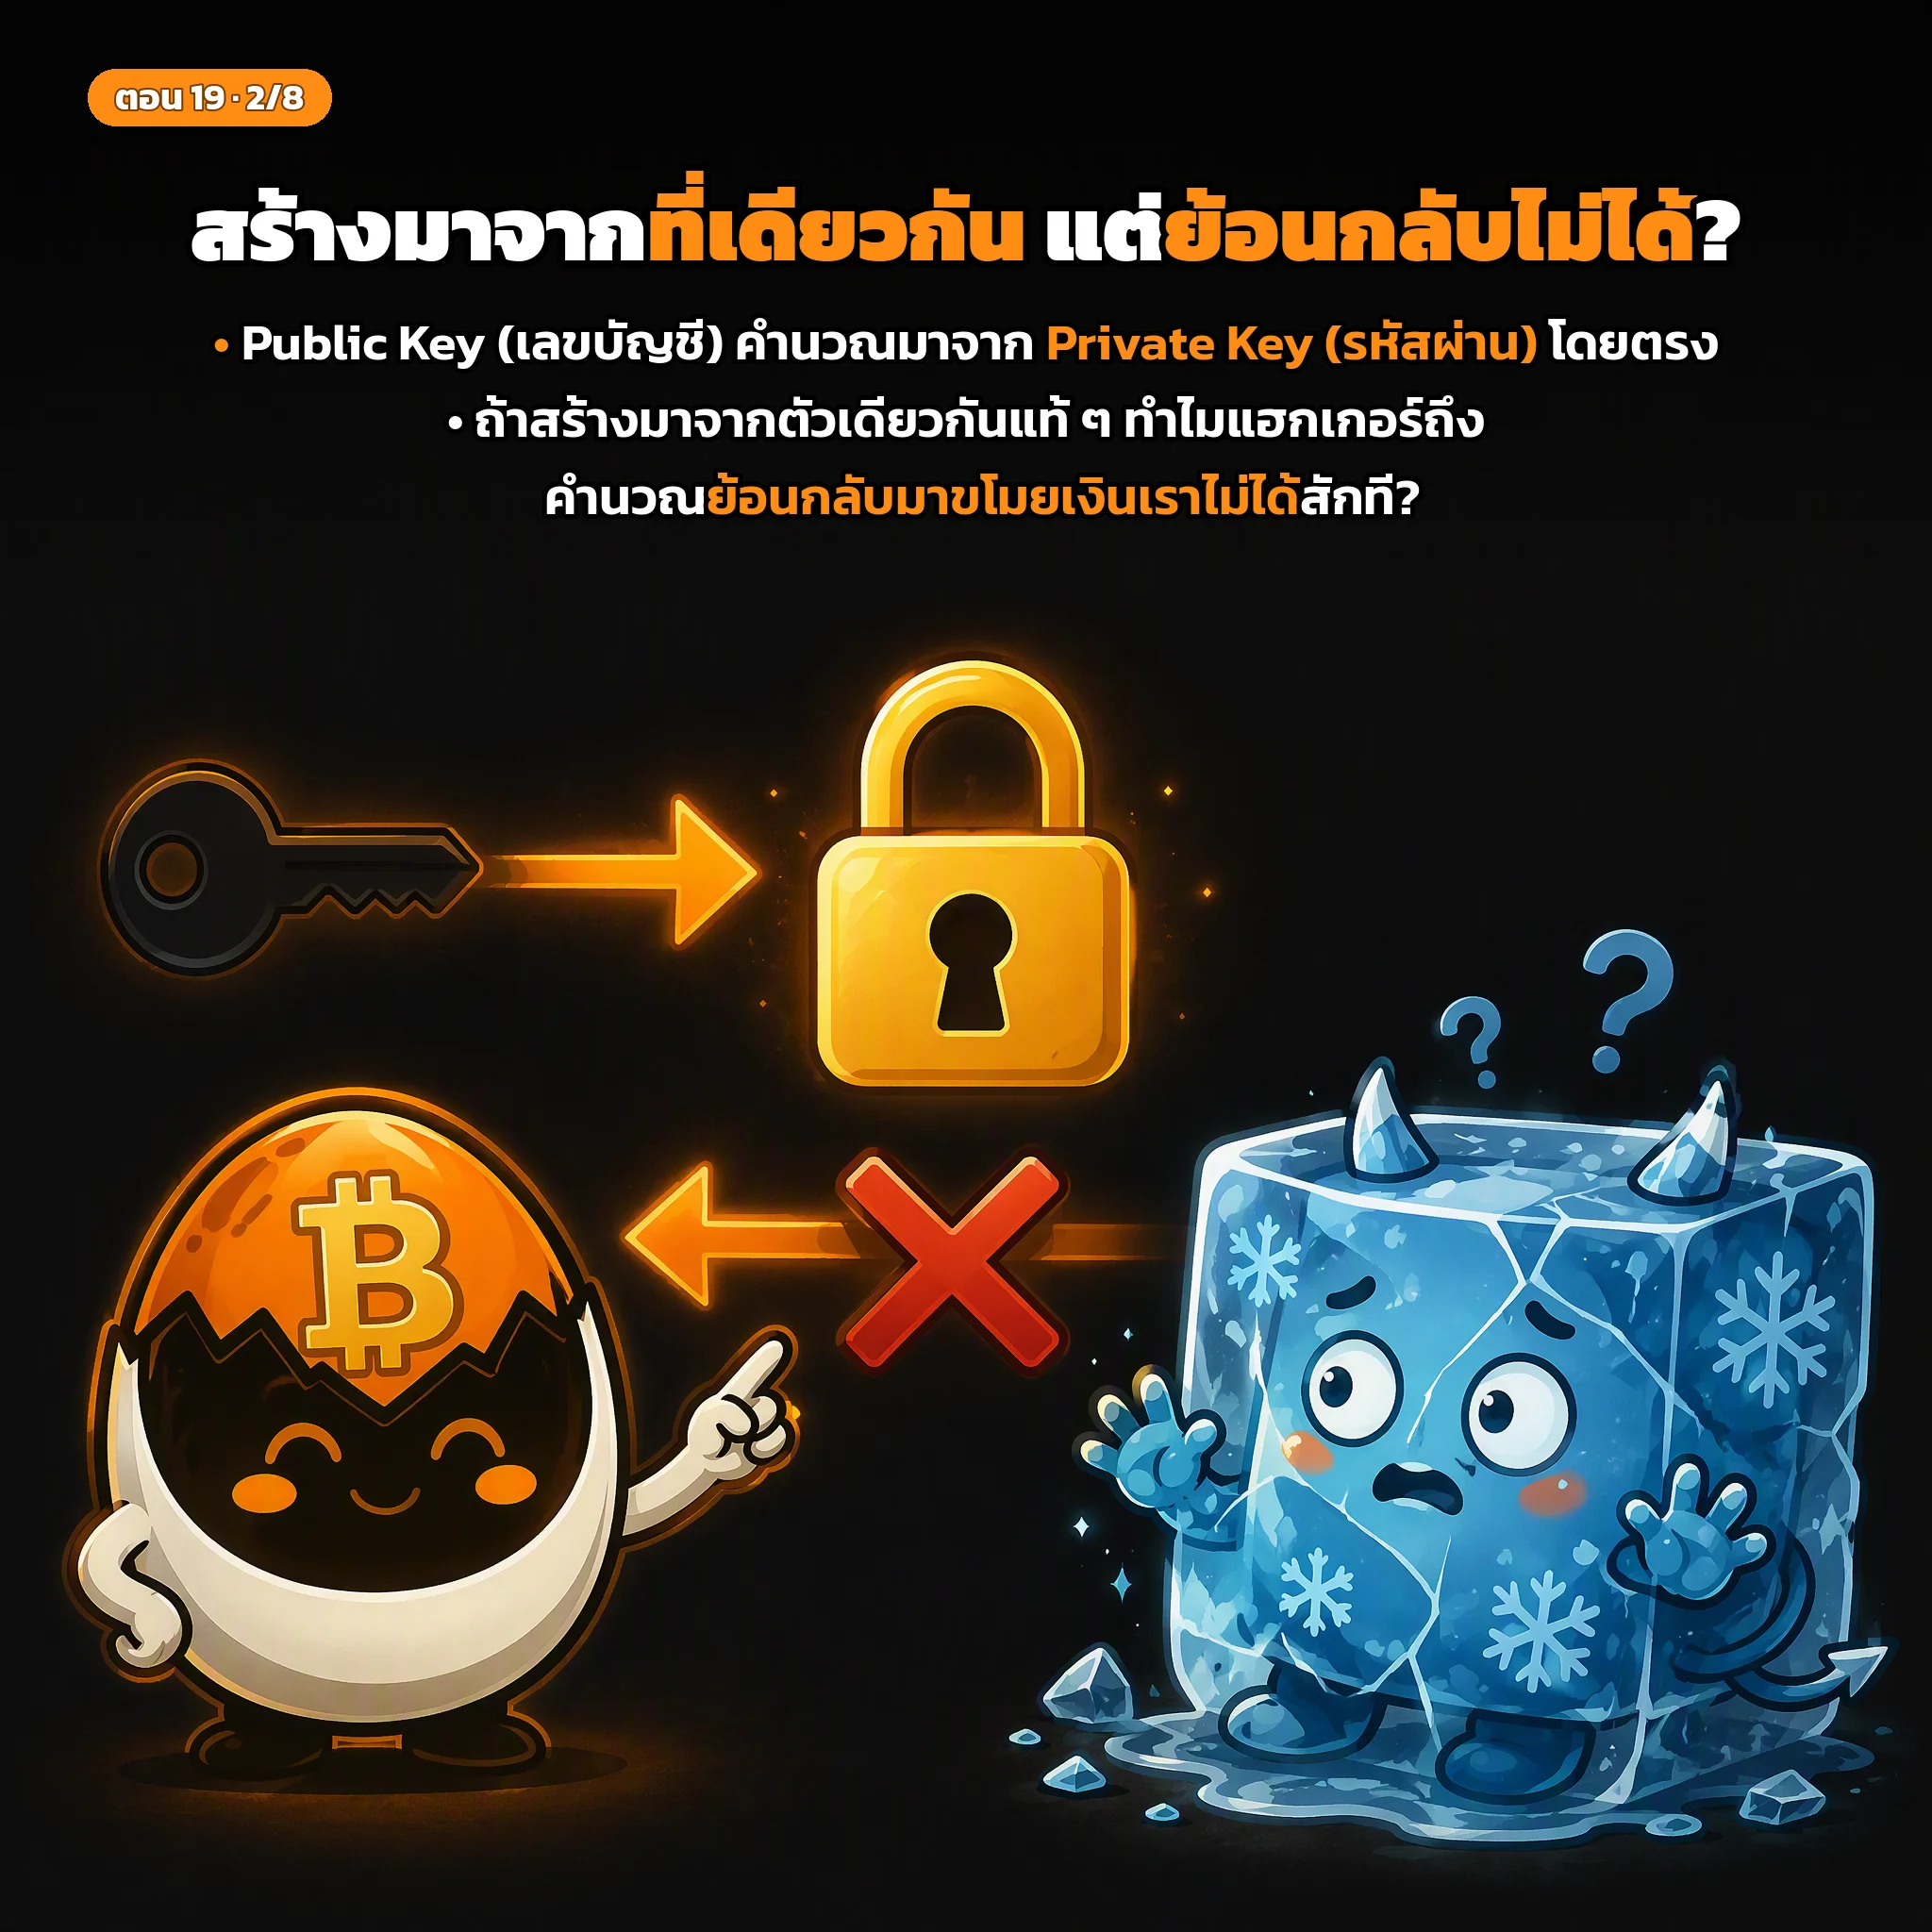
Public Keys are computed from Private Keys using Elliptic Curve Cryptography (ECC) over the curve secp256k1:

$$y^2 = x^3 + 7 \pmod p$$

📈 Point Multiplication
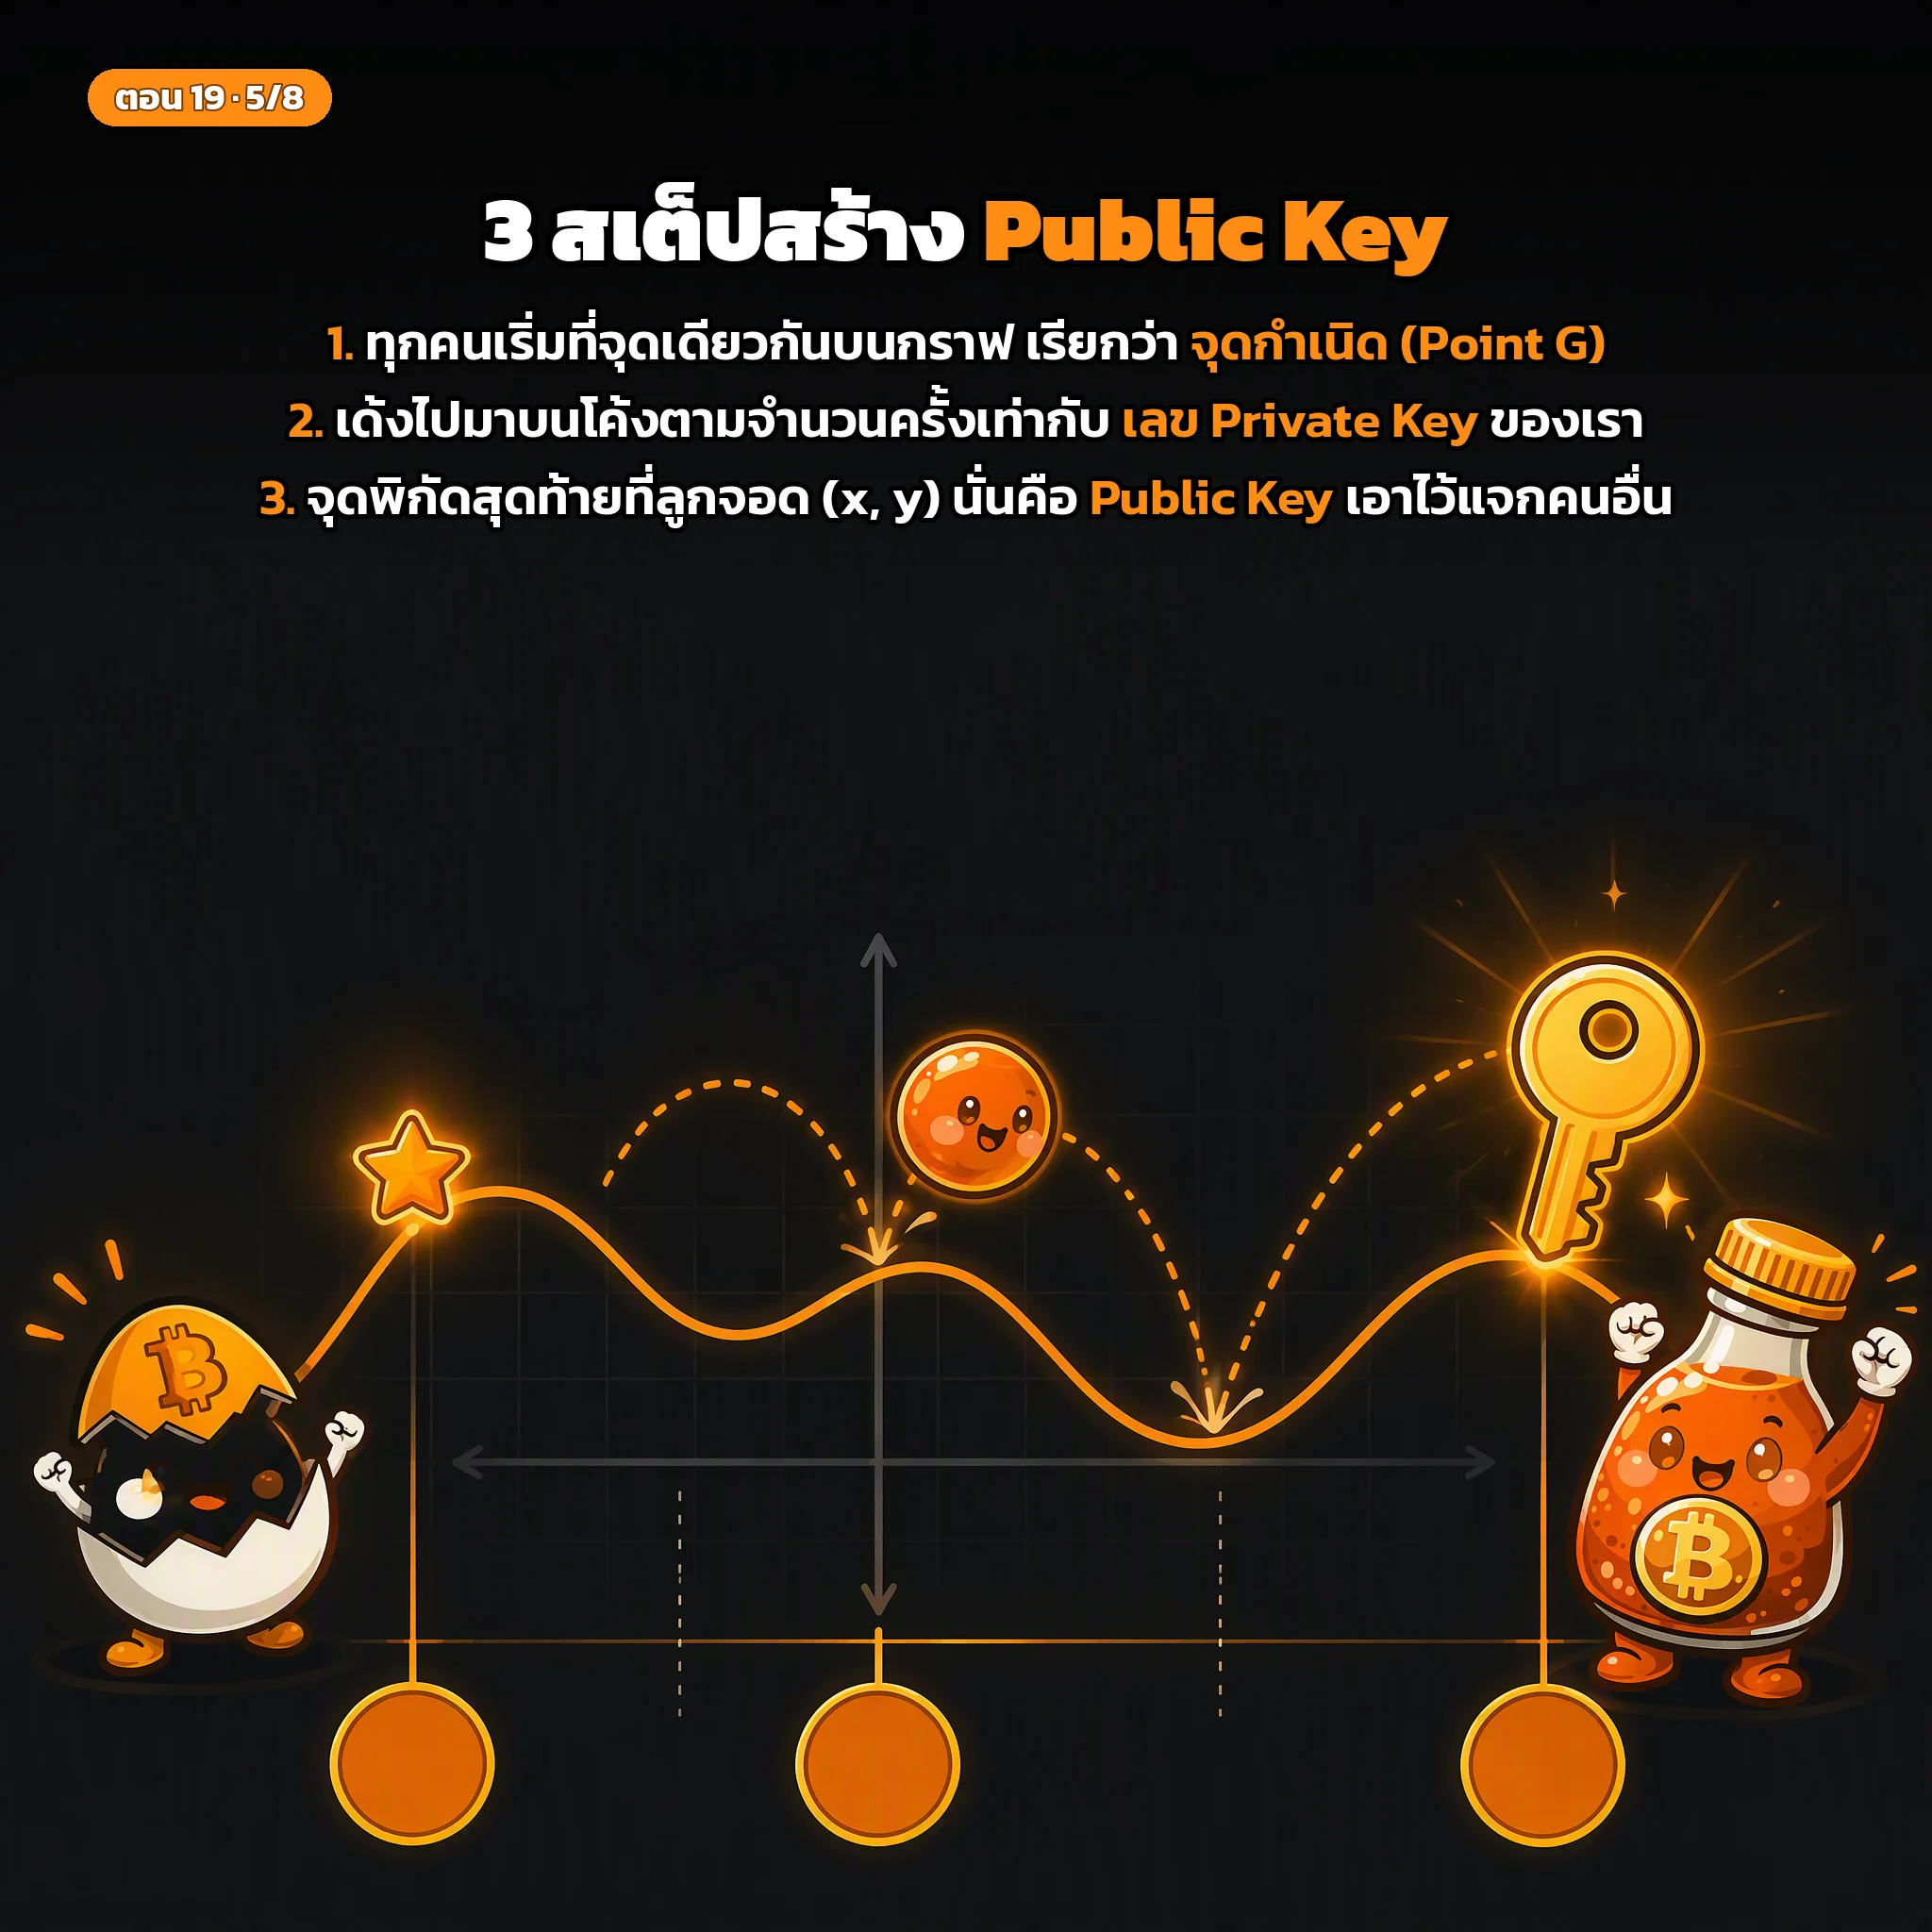
Given a generator point $G$ on the curve and your private key scalar $k$, the public key point $K$ is calculated as: $$K = k \cdot G$$

Point multiplication on an elliptic curve is a trapdoor function: easy to calculate $K$, but practically impossible to calculate $k$ given $K$ (Elliptic Curve Discrete Logarithm Problem).

🧠 Today's Key Takeaway

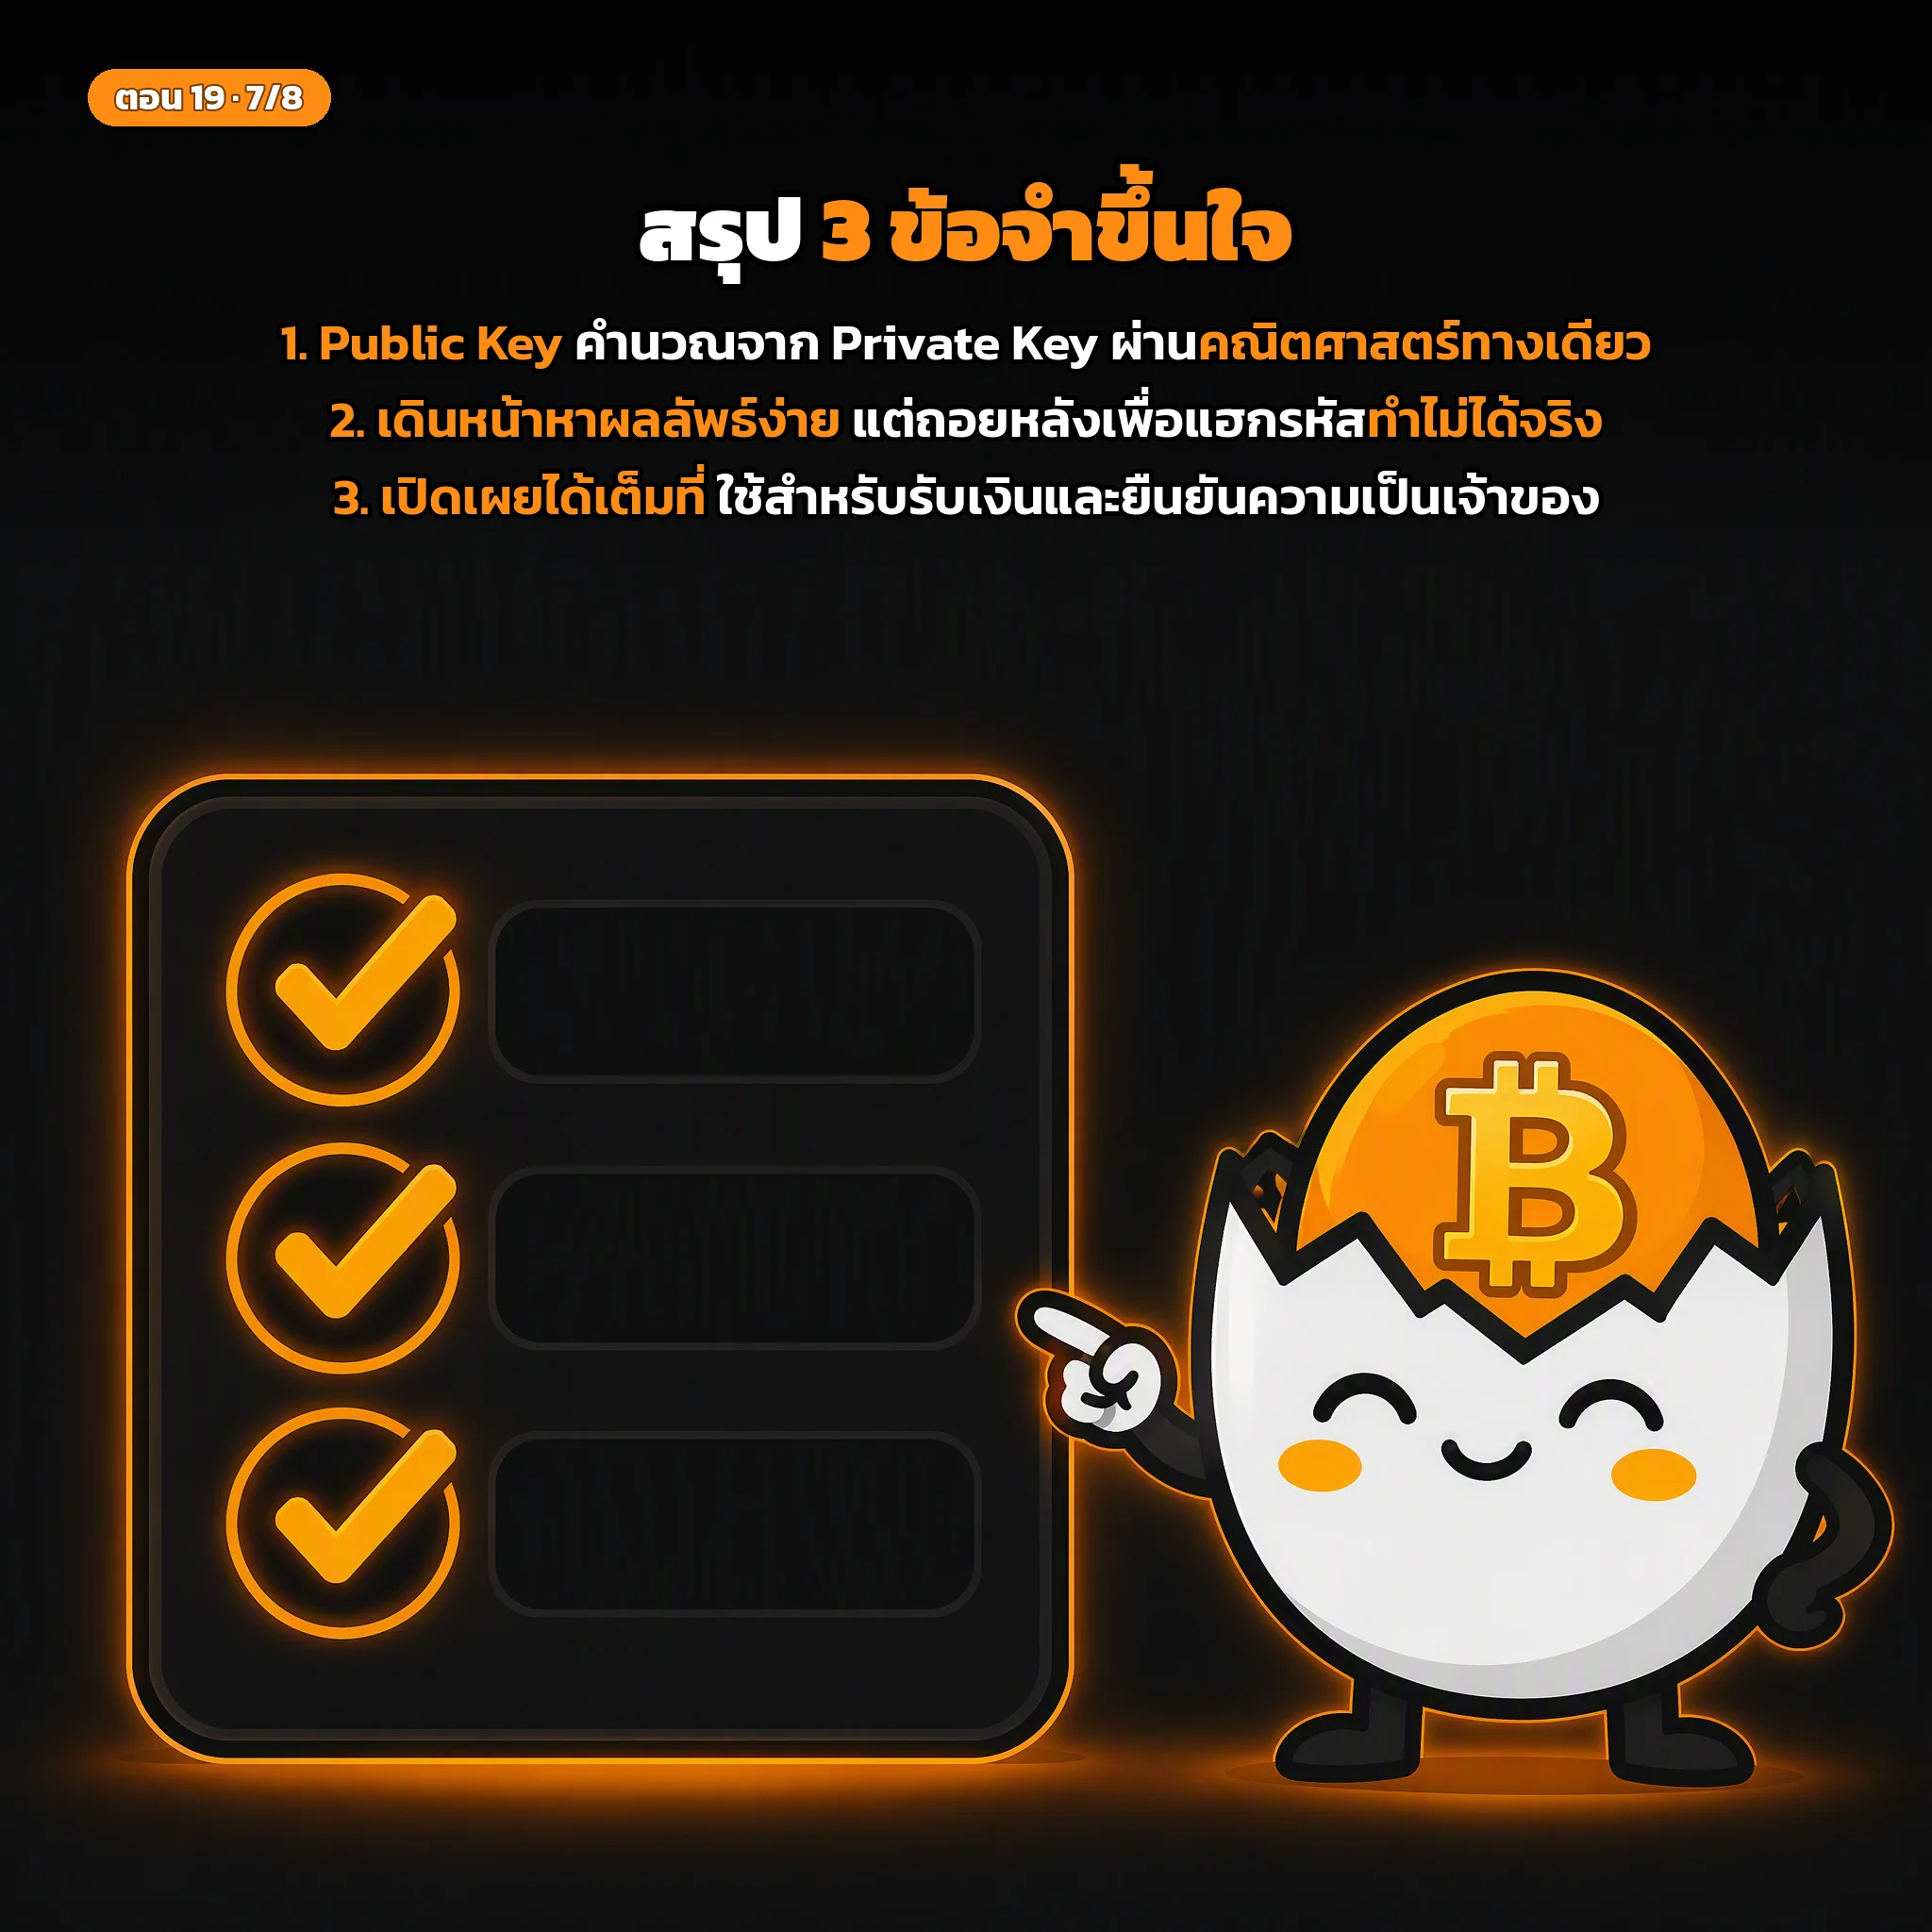
  • Public keys are point coordinates on the secp256k1 elliptic curve.
  • Elliptic curve multiplication provides cryptographic trapdoor security.
🖼️ All slides for this episode (8 slides)

Slide 2 for Episode 19Slide 3 for Episode 19Slide 4 for Episode 19Slide 5 for Episode 19Slide 6 for Episode 19Slide 7 for Episode 19Slide 8 for Episode 19
Review Understanding

End of Chapter Quiz

Answer 1 questions to test your understanding

1. Which elliptic curve standard does Bitcoin use to generate public keys?

✅

Finished reading this episode?

Mark as read to track your learning progress